TherapyVault · secure video platform for therapy
A private video platform where therapists safely share recorded sessions with their own clients. No public URLs, no YouTube link with "anyone with the link can view". Everything sits behind signed URLs with granular per-client access grants, optionally time-limited, view-limited or download-limited.
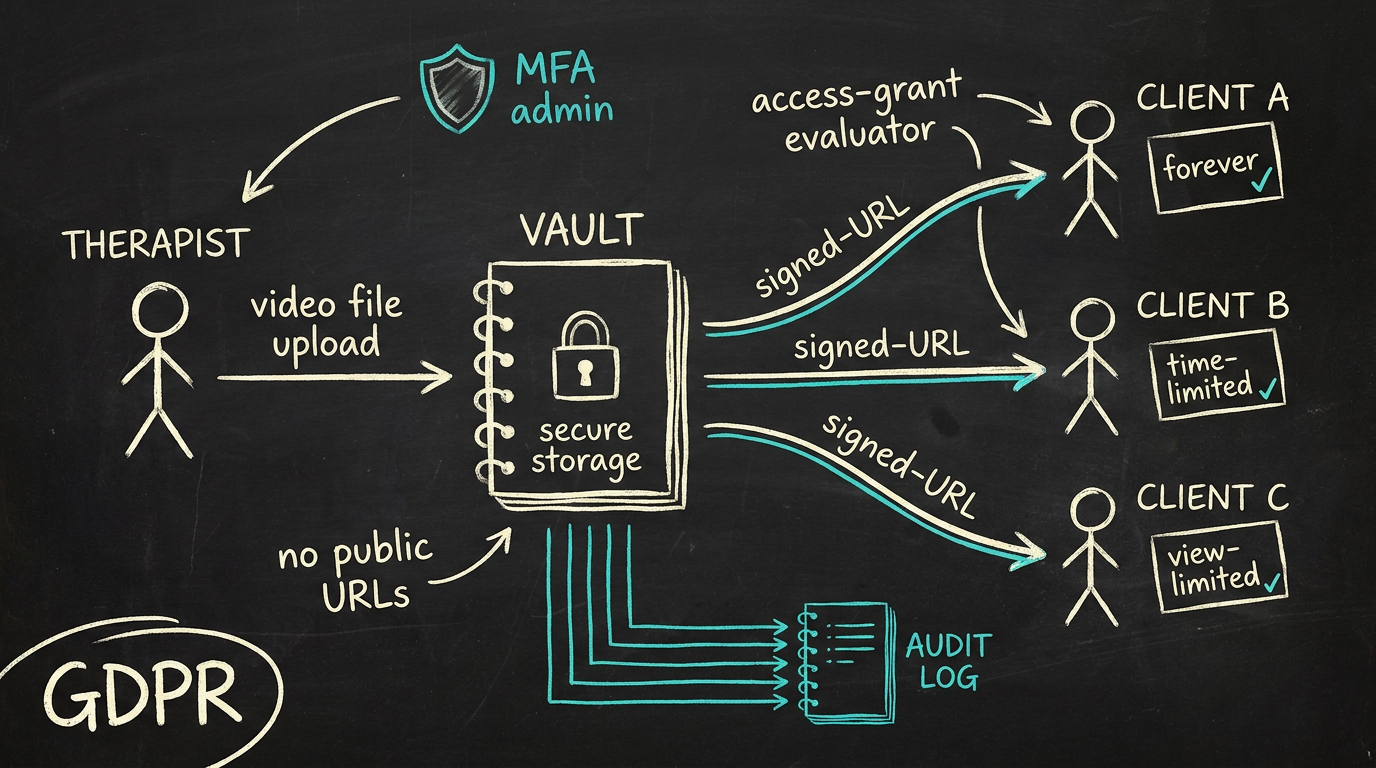
Whiteboard sketch · the shape of the system
Problem
WeTransfer is not GDPR-compliant for healthcare data. YouTube unlisted is not access control. SharePoint is enterprise overkill. Vimeo Pro
- Memberstack is fragile and expensive.
TherapyVault is the specific answer: one place where the therapist uploads and the client watches securely, with the legal and technical foundation a healthcare context demands.
What's in v0.1
| Area | Status |
|---|---|
| Auth | Email+password, password reset, MFA (TOTP), session management, RBAC |
| Video upload | Resumable multipart (tus protocol) up to 10 GB, to R2 / S3 / MinIO |
| Video streaming | Signed-URL playback with range support, no public URLs |
| Access control | Per grant: forever / time-limited / view-limited / download-limited |
| Coupons | 5 types: free access, % off, fixed off, download credit, view credit |
| Payments | Stripe (one-time + subscriptions) + Mollie stub behind a PaymentProvider interface |
| Dashboards | Therapist, Client, Admin |
| GDPR | Data-export ZIP + scheduled deletion with grace period |
| i18n | EN + NL from day one (next-intl) |
| Audit log | Every sensitive mutation is recorded |
Stack
@tus/serverPaymentProvider interface with Stripe-live + Mollie stub behind itSecurity primitives
No public URLs. Every video stream goes through a signed URL that the server only issues after an access-grant check. Range headers are supported without the URL ever leaking outside the session.
MFA mandatory for admins. Pairing a TOTP app is a first-login requirement; no access to admin dashboards without it.
Argon2id as the password hash with memory-hard parameters.
GDPR by design. Client-data export as a ZIP, account deletion via a scheduled job with a grace period, an AuditLog table for all sensitive mutations.
Payment-provider abstraction. Stripe live, Mollie behind the same interface: switch to iDEAL without touching the business logic.
Roadmap
| Version | What |
|---|---|
| v0.1 (now) | All critical security primitives, production-deployable |
| v0.2 | UI polish, multi-bitrate HLS transcoding, push notifications, real email provider |
| v0.3+ | Custom domain per therapist, white-label, live sessions |
Status
v0.1 release candidate. An SMTP provider and real email templates are the next step toward launch. Client and specific use case under NDA.